
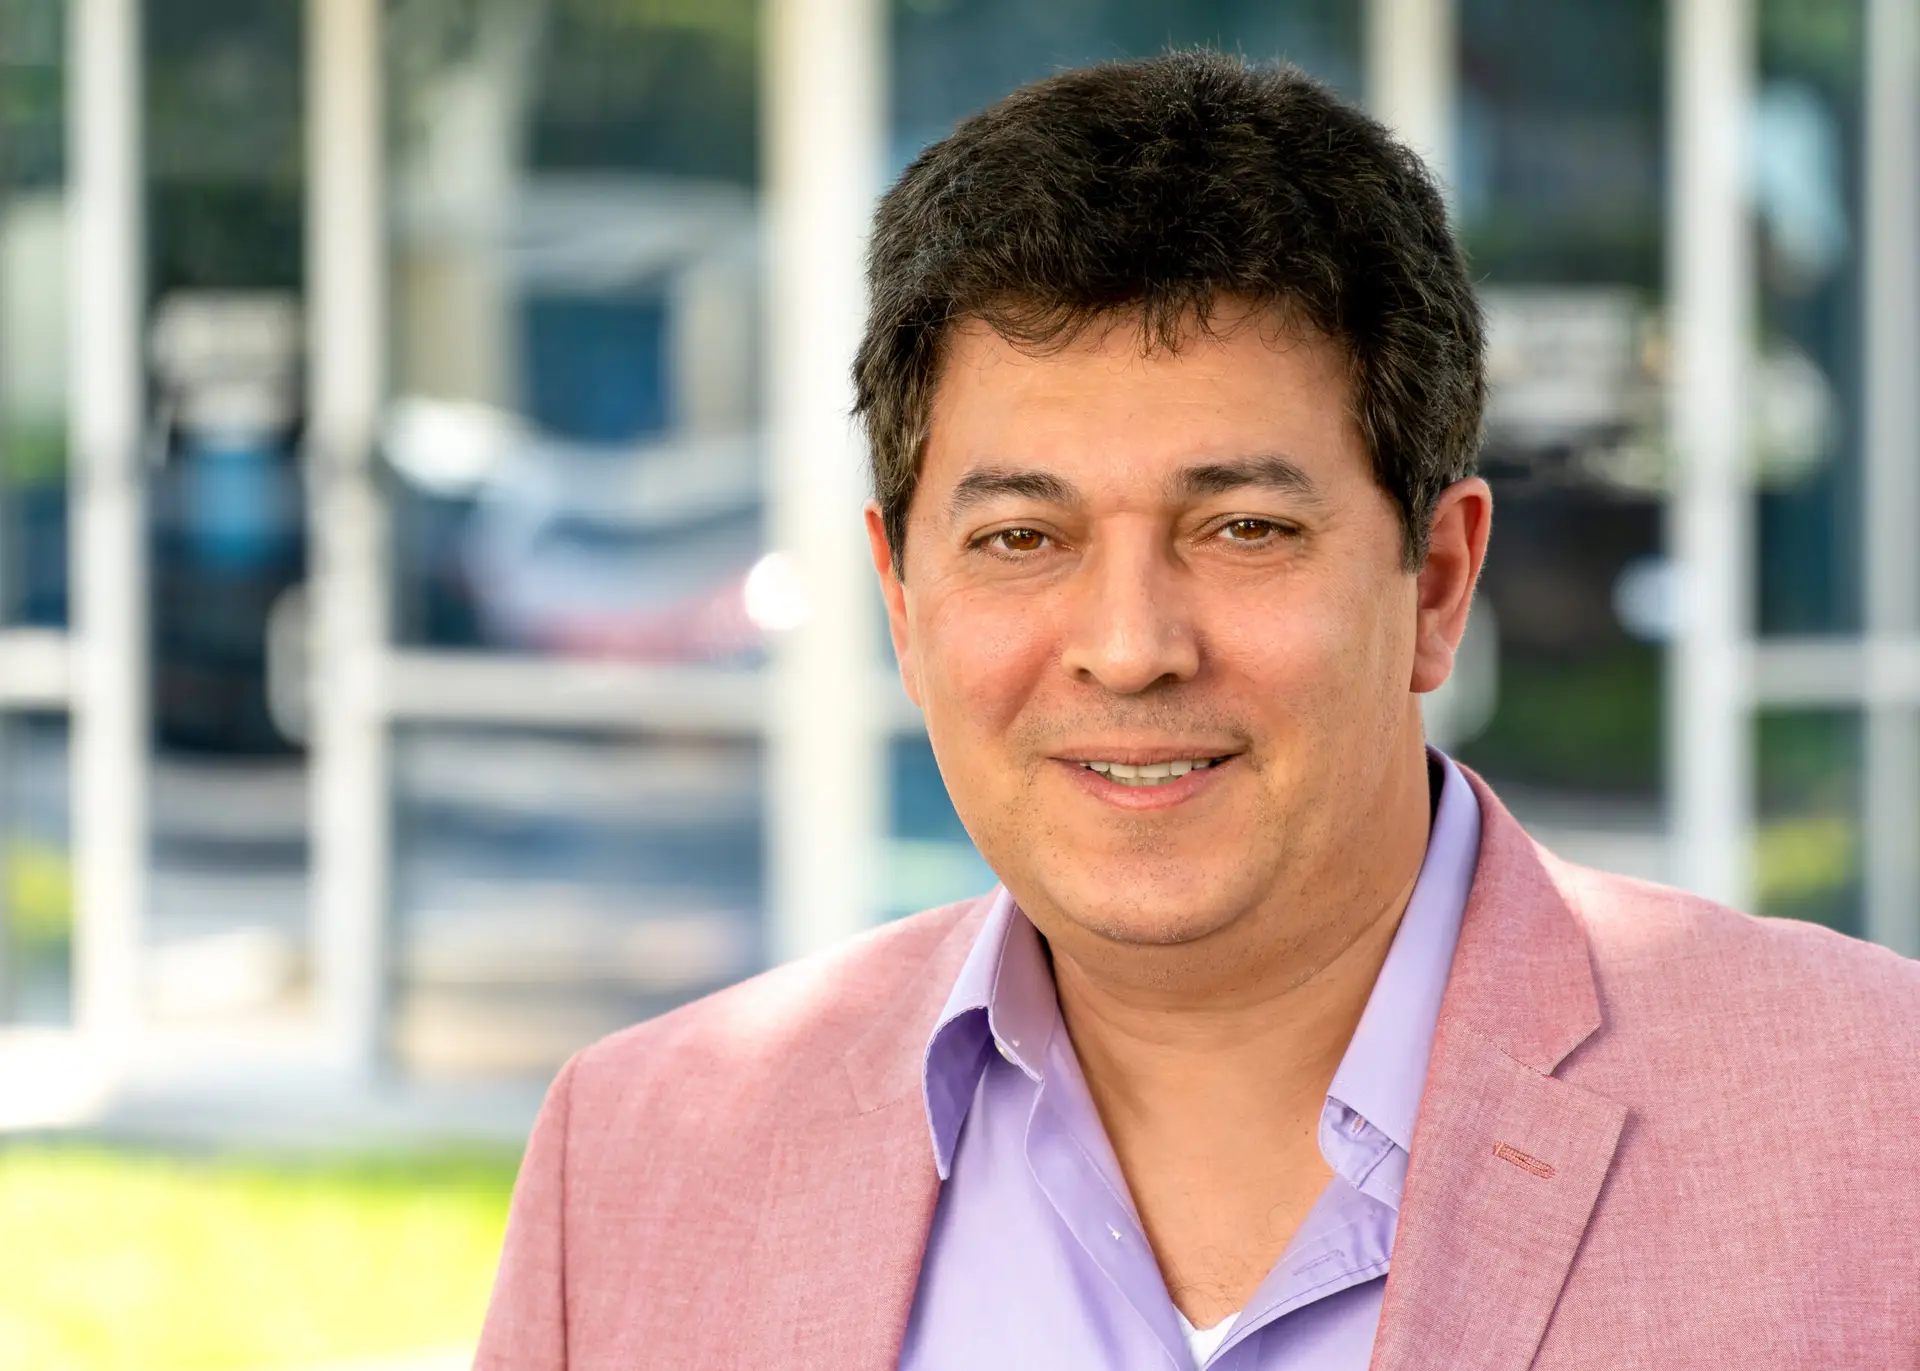
Chief Security Officer
Mohamad Foustok
Mohamad has led the development of secure software and mission-critical security systems for more than 25 years. He designed the first in-browser crypto module to receive FIPS 140-2 certification and the only FIPS 140-3 compliant solution for securing commercial devices in classified spaces.
His career includes direct collaborations with the NSA, CIA, DISA, and DoD to deliver highly secure communication systems, including one of the only software platforms in the world validated to thwart both Spectre and Meltdown attacks per NSA review.
He earned a Bachelor of Engineering degree from Imperial College London and holds a Master's degree along with PhD studies in Computer Science (ABD), maintaining a 4.0 GPA.
Credentials
- BE, Imperial College London
- MS, Computer Science (4.0 GPA)
- PhD studies in Computer Science (ABD)
- Designer of the first FIPS 140-2 in-browser crypto module
Areas of expertise
- FIPS 140-2 and FIPS 140-3 cryptographic module validation
- Secure software architecture
- Mission-critical systems security
- Medical device cryptography
- Spectre and Meltdown mitigation
Articles by Mohamad Foustok
- The 5 Riskiest Medical Devices in 2026, According to New Research
Forescout's 2026 Riskiest Devices report names the five riskiest medical devices in 2026 and what the list means for manufacturers' FDA cybersecurity programs.
March 24, 2026
- Medical Device Encryption for Non-Engineers
A plain-language guide to medical device encryption for QA and regulatory teams: symmetric vs asymmetric, key management, and quantum implications.
January 8, 2026
- Balancing Security Controls with Usability in Medical Devices: A Risk-Based Approach
How to balance medical device cybersecurity controls with clinical usability: a risk-based method, emergency access patterns, and what FDA expects to see.
September 4, 2025
- STRIDE for Medical Devices: A Complete Threat Modeling Framework
STRIDE for medical devices in practice: how to run the session, the six questions to ask of each element, the controls each one points to, what to hand FDA.
July 22, 2025
- Security Architecture as the Foundation of your Medical Device
Explains why secure architecture decisions early in development prevent costly rework and position medical devices for smoother FDA cybersecurity reviews.
June 18, 2025
- Secure Your Medical Device with Cybersecurity Controls
How to implement cybersecurity controls for medical devices: choose, build, and verify each control, with every one traced to a specific threat in your model.
February 20, 2025
- Master Data Flow Diagrams for Medical Devices: 4 Critical Components
How to create data flow diagrams for medical devices: the four components plus trust boundaries, the steps to build one, and how DFDs feed FDA's threat model.
February 18, 2025
- Medical Device Security Architecture: How to Build the View FDA Expects
How to build the medical device security architecture views FDA reviewers expect: the four views in Section V.B.2, trust boundaries, controls, and standards.
February 14, 2025
- How to Establish Patch Management and Security Update Process
How to establish a patch management and security update process for medical devices that meets Section 524B and FDA's cybersecurity management plan elements.
February 11, 2025
- A Comprehensive Guide to Threat Modeling for Cloud-Connected Medical Devices
Threat modeling for cloud-connected medical devices: model the device, app, and cloud, apply STRIDE at trust boundaries, score exploitability, document for FDA.
February 10, 2025
- Ensuring Secure Software Updates for Medical Devices
The update path is privileged code execution shipped to every device. Here is the architecture that keeps medical device software updates secure.
July 18, 2024
- New Cybersecurity Regulations Make Remote Software Updates Practically Mandatory
Why remote software updates are practically mandatory for FDA cyber devices under Section 524B, and what the 2026 cybersecurity guidance expects you to show.
July 18, 2024