IEC 62304 to FDA eSTAR: A Software Documentation Guide
Map IEC 62304 to FDA eSTAR software documentation. Compare Basic and Enhanced levels and align requirements, risk management, testing, and traceability.
Using IEC 62304 throughout the software lifecycle when preparing an FDA eSTAR submission can reduce the need for many “one-off” documents that would otherwise have to be produced specifically to satisfy FDA’s software documentation recommendations. In other words, you can often reuse documentation instead of creating a separate “FDA version” if IEC 62304 has been consistently applied and the documents address FDA’s submission recommendations.
Summary
- Process-to-deliverable mapping - This short white paper reviews how using IEC 62304 throughout development maps onto the recommended software documentation for devices (those listed on FDA’s eSTAR form).
- Documentation level determination - NOTE: FDA recommends that the Basic versus Enhanced decision be made based on the probable risk from a software failure before risk controls, not based on the IEC 62304 safety class. Enhanced level submission documentation adds the Software Design Specification compared with Basic submission documentation, where it is not routinely recommended for submission.
- The 10 essential documents - This paper also lists all of the 9 (Basic) and 10 (Enhanced) recommend FDA documentation items and reviews which IEC 62304 activities and deliverables map onto each item.
- Efficiency through alignment - Following IEC 62304 from the first step (development planning) through to software release, much of the recommended FDA documentation can be produced during development and organized for submission.
- Practical implementation - By structuring documentation in this way from the start, potential rework when preparing FDA submissions can be avoided.
What you'll learn: How to generate FDA eSTAR software documentation directly from your IEC 62304 development process, thus saving effort and helping you identify what is needed for your submission
Introduction
If your device has software, you have probably encountered a situation where your team followed IEC 62304 and documented everything, only to spend weeks “reformatting” this documentation to comply with FDA’s eSTAR submission guidelines. Requirements are reformatted, design documentation is reordered, test records are repackaged, and essential information ends up in more than one place.
In short, IEC 62304 tells you what to do and when. The FDA wants to know that your software will be safe and effective, and asks for documentation that shows this. By understanding how these two go together, you can streamline your work and avoid additional documentation effort that delays your device submission and creates problems down the line when Regulatory and Quality have to sort out gaps in documentation.
Many companies don’t realize that FDA eSTAR requirements and IEC 62304 are not at odds, but go hand in hand. If you follow IEC 62304, you can produce much of the eSTAR documentation FDA wants during development. In fact, there’s a process-to-document mapping between IEC 62304 and FDA eSTAR documentation, which can reduce duplicated effort or redundant documentation if you understand the relationship.
In this guide, you’ll learn which IEC 62304 activities produce each eSTAR document, how to write your documents to address the standard and FDA’s recommendations at once, and tips and tricks to write your documents efficiently, so you spend less time preparing FDA submissions.
To learn more about the eSTAR submission process, the form itself, and what reviewers look for, see our book chapter on understanding eSTAR requirements.
What's the difference between Basic and Enhanced documentation levels?
The distinction between Basic and Enhanced level documentation reflects the risk your device poses to patients, users or others in the environment of use. A blood glucose meter doesn’t pose the same risk as an implantable pacemaker. The documentation FDA recommends is proportional to the risk your device poses.
Documentation Level Evaluation
Documentation Level Evaluation: explain why Basic or Enhanced level documentation is appropriate, depending on the risk posed by your device.
Accordingly, the first thing FDA asks for in your software documentation is a Documentation Level Evaluation, in which you identify whether you submit at the Basic or Enhanced level, and explain why that level is appropriate.
The FDA’s 2023 Software Documentation Guidance creates a decision point about the level of documentation needed for software functions in medical devices. To use this decision point, ask the following question: Could a failure or flaw of your device software function present a probable risk of death or serious injury to a patient, user, or others in the environment of use? If the answer is yes, Build documentation at the Enhanced level. If the answer is no, the Basic level is appropriate, subject to FDA’s category-specific recommendations below.
Note that the decision about documentation level is distinct from decisions about the IEC 62304 software safety class (see Section 4.3), and is based on the answer to the above question looking at the raw, unmitigated risk (i.e., before risk control measures are put in place) including reasonably foreseeable misuse and inadequate cybersecurity. Document both decisions on their own terms. A Class B item in IEC 62304 could be documented at the Enhanced level per FDA guidance, and a Class C item documented at the Basic level.
Scope Difference Between Levels
Basic Level: recommends nine (9) documentation items and is appropriate when Enhanced documentation does not apply under the probable risk of death or serious injury assessment and FDA’s category-specific recommendations. Examples of Basic Level software may include, but are not limited to, software used in non-contact thermometers, blood pressure cuffs, and some medical software that supports diagnostic decision making, depending on intended use and the risk assessment.
Enhanced Level: recommends ten (10) documentation items and is appropriate for software where a failure could present a probable risk of death or serious injury to a patient, user, or others in the environment of use. Examples include, but are not limited to the software used in ventilators, pacemakers, infusion pumps, and some in-vitro diagnostic (IVD) blood screening assay systems. FDA generally recommends the Enhanced Level of documentation for Class III devices, as well as device constituent parts of combination products, unless the applicant provides an appropriately detailed justification for a lesser level.
These are documentation items, not a fixed number of separate files. The Enhanced Level raises the bar by adding Software Design Specification (SDS) submission documentation, more robust (unabridged) Configuration Management and Maintenance Plans (or an applicable Declaration of Conformity to FDA-recognized IEC 62304 clauses), and more detailed (read: less summarized) Unit and Integration Level Test Protocols and Reports (i.e., include both expected and actual results).
DoKeep in mind that it’s important to decide early in the development cycle which documentation level requirements your project will adhere to (basic or enhanced), as this decision will dictate many things throughout the course of your development activities, such as your timeline, resource allocation, and documentation approach.
The 10 eSTAR Software Documents
The FDA has different eSTAR sections for software documentation as part of its medical device premarket review process, and each section serves to demonstrate that the device is both safe and effective. These various eSTAR documentation items can draw on your IEC 62304 development process.
Below is a general overview of the first 4 eSTAR documentation items:
Document 1: Documentation Level Evaluation
Purpose: To justify, based on risk, which documentation level is appropriate (basic or enhanced) for your software.
Content Requirements: The level you’re choosing, a rationale based on the intended clinical use, and cross-references to support your rationale (e.g. Risk Management File, Software Description).
IEC 62304 Source: Section 4.3 (Software safety classification), Section 7.1 (Analysis of software as part of a hazardous situation) and other ISO 14971 risk management information.
Key Elements: Claim about documentation level, description of hazardous situations resulting from software failures, impact on patient, user or others before risk controls are applied
Practical Tip: accomplish this early on and put significant effort in to accomplish this with high rigor (the FDA may question a Basic claim if the risk assessment supports Enhanced documentation)
Document 2: Software Description
Purpose: provide a high level overview of the software that provides enough detail to understand what the software does, its features, and its environment
Content Requirements: primary features/capabilities, operating environment(s), hardware platforms, inputs/outputs (including source/destination), user interaction(s), clinical workflow(s), diagrams (e.g. block, flow, state).
IEC 62304 Sources: 5.1 Software development planning and 5.3 Software architectural design
Key Elements: System context diagrams, deployment architecture, user workflows, interoperability specifications, AI/ML methodology if applicable
Practical Tip: this is the front door document for reviewers, go the extra distance to ensure this document is immaculate Think of this document as the software “executive summary”. And if your software incorporates AI/ML or special interfaces/interoperability with other devices, be sure to highlight those and the approaches you are taking in this document.
Document 3: Risk Management File
Purpose: To demonstrate a systematic approach to identifying and addressing software related hazards in an ISO 14971 compliant fashion.
Content Requirements: A risk management plan that defines risk acceptance criteria, a risk assessment including identification, evaluation, risk controls, a benefit risk analysis where applicable, and a risk management report that demonstrates the plan has been appropriately implemented and the overall residual risk is acceptable. Traceability from hazards to risk controls to verification must be demonstrated.
IEC 62304 Sources: Integrated throughout development, Section 7 Software risk management process and Clause 4.3.
Key Elements: Definition of hazardous situations, demonstration that risk controls have been verified and traceability linking hazards to requirements to design to tests.
Document 4: Software Requirements Specification (SRS)
Purpose: To provide a comprehensive list of requirements of your software, that can be traced during development activities.
Content Requirements: Functional requirements describing software behavior, performance, user, hardware and other software interfaces, requirements derived from risk analysis (safety requirements), security requirements, software limits and default values and ranges of data.
IEC 62304 Source: 5.2 Software requirements analysis.
Key Elements: Unique ID for each requirement, clear pass/fail criteria, traceability to system level requirements and risk controls, verification method.
Practical Tip: All requirements must be verifiable. Use "shall" statements and avoid subjective language. Make sure requirements are measurable.
Document 5: System and Software Architecture Design (the eSTAR "Architecture Design Chart")
Purpose: To give an overview of the system architecture, including how modules relate to one another, data flow through the system (including inputs and outputs), and user interfaces and interactions with external systems. This includes underlying IT infrastructure and deployment topology.
Content Requirements: Diagram of system modules and software layers (including schematics of modules, software and system layers and their interfaces), demonstrating dependencies and relationships between modules, data flow including inputs and outputs across all modules as well as user interfaces and interactions with external systems. Include underlying IT infrastructure and deployment topology.
IEC 62304 Source: 5.3 Software architectural design
Key Elements: Software Architecture: Component & Sequence Diagrams, ICD, Deployment Diagram, Cybersecurity Architecture Description
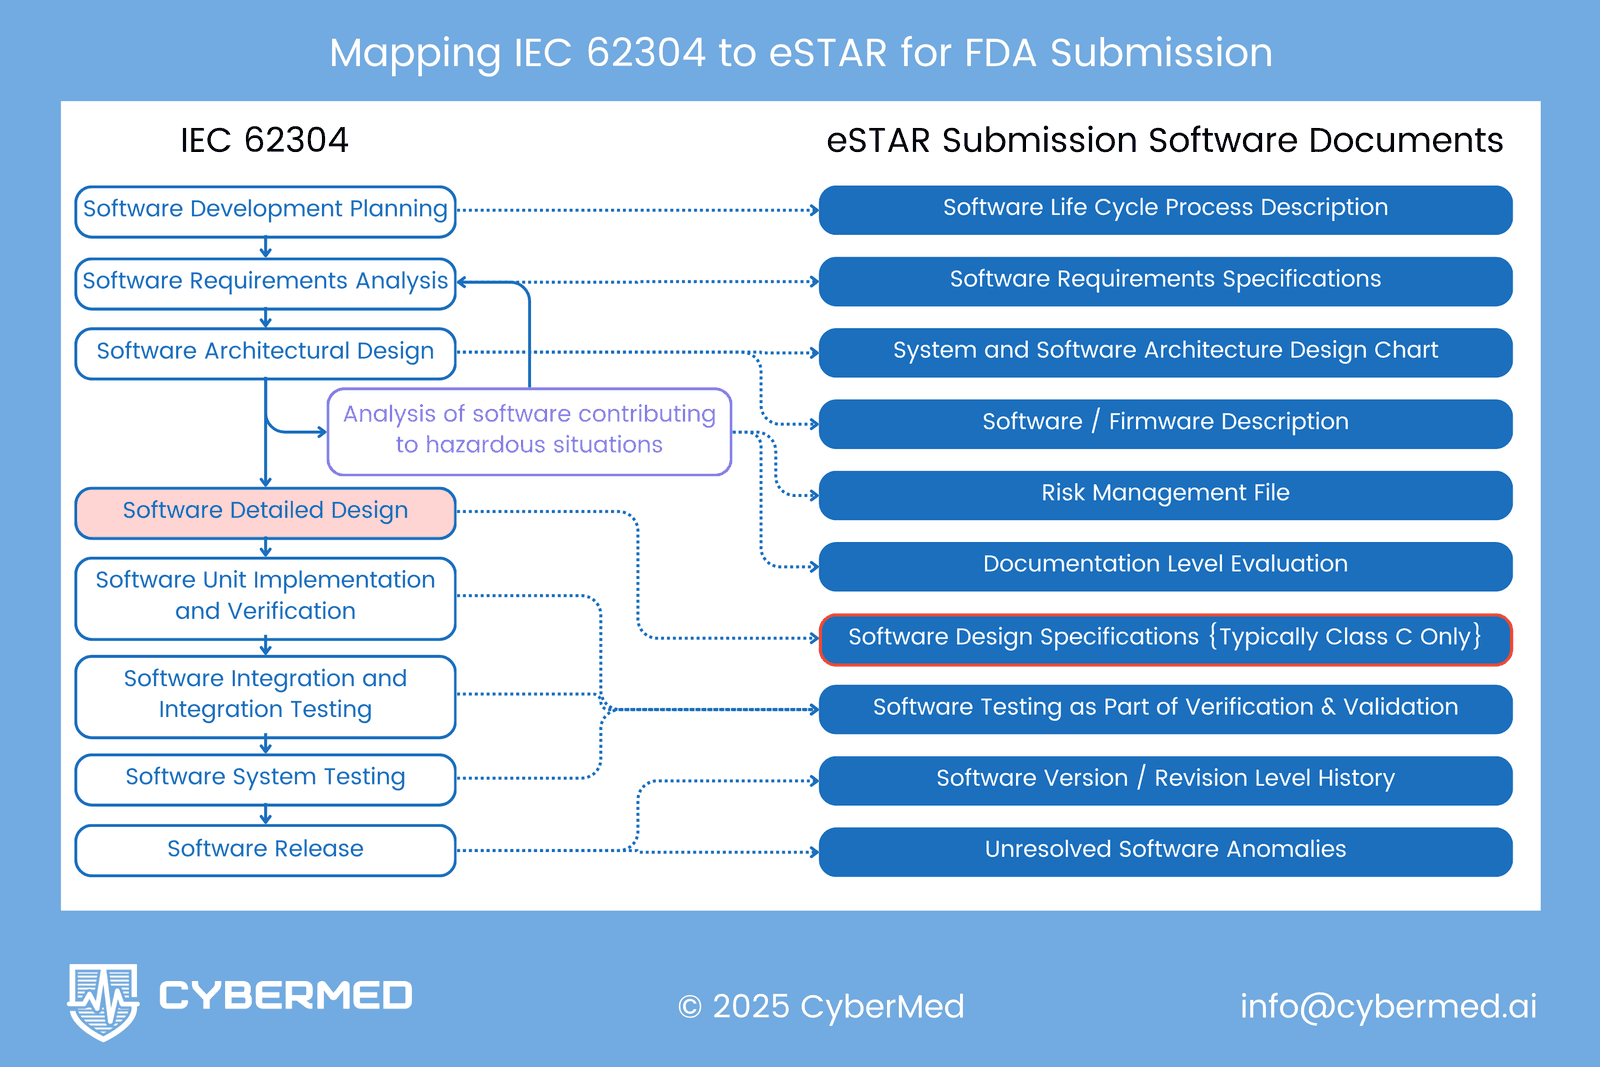
Note: Analysis of software contributing to hazardous situations bridges architectural design to multiple deliverables. It feeds Software Description, Risk Management File, AND Documentation Level Evaluation. This analysis is foundational for safety classification.
Practical Tip: Use a standard notation such as UML or SysML language to maintain consistency in documentation. Ensure your diagrams are readable and clear; one should not need to zoom in excessively! Rather than crowd everything in one diagram, multiple, not overly dense diagrams each revealing different aspects of the software design would probably be most effective.
Document 6: Software Design Specification (SDS) [Enhanced Level Only]
Purpose: To provide a technical design description indicating how the software design implements each software requirement.
Content Requirements:
- Detailed design description of each software component/module.
- Detailed description of algorithms and data structures.
- Implementation detail.
- Traceability evidence to demonstrate that the SDS fully and accurately reflects the Software Requirements Specification (SRS).
IEC 62304 Source: 5.4: Software detailed design.
Key Elements: Unit-level design, detailed algorithms, interface implementations, data structure definitions
Important: This is NOT a document limited to Class C software. The FDA Enhanced Documentation level depends upon FDA’s documentation-level risk assessment (which may or may not align with the IEC 62304 classification). An SDS is recommended for submission at the Enhanced level. For devices needing only a basic level of documentation, an SDS is not routinely recommended for submission. However, it needs to be included in the design and development file (the DHF under the former regulation) and made available upon request for FDA reviewers.
Practical Tip: FDA reviewers will look for evidence that the code was written according to plan (SDS) rather than evidence that an SDS was written after the fact to explain existing code. Therefore, it is recommended to write your SDS prior to beginning implementation, and use it as a development tool.
Document 7: Software Development, Configuration Management, and Maintenance Practices
Purpose: Describe the process used to develop the software.
Content Requirements:
For Basic level
- A general description of the software development life cycle, coding standards, development methodologies, and software development tools.
- The expected deliverables from development.
- Traceability expectations from requirements through design, verification, risk mitigation activities and other design inputs.
- Configuration management and change control processes.
- Software maintenance and regression strategies.
For Enhanced level
- All Basic level documentation.
- Complete Formal Configuration Management Plan.
- Complete Software Maintenance Plan.
- Additional detail regarding tools and procedures used.
IEC 62304 Sources: Demonstration of compliance with Software Development Planning (Section 5.1), Software Maintenance Process (Section 6), and Software Configuration Management (Section 8).
Key Elements: Core components should include software development and configuration plans, change control procedures, traceability methods, and regression test plans.
Alternative Approach: Declaration of Conformity with applicable sections of the FDA-recognized version of IEC 62304 (as identified by the FDA). For the Basic level, this includes Sections 5.1.1, 5.1.2, 5.1.3, 5.1.6, 5.1.7, 5.1.8, 5.1.9, as well as Sections 6 and 8. For the Enhanced level, this includes all of Section 5.1, Section 6 and Section 8.
Practical Tip: Where possible, references to relevant Quality Management System (QMS) procedures may be used to avoid duplication.
Document 8: Software Testing Documentation
Purpose: Demonstration of verification and validation evidence for meeting all software requirements.
Content Requirements:
For Basic level
- An overview of unit, integration and system level testing, and system level test protocols documenting objectives, observed versus expected results, pass/fail criteria.
- Final system level test report showing acceptable completion of testing protocol.
- Software version tested and an overall pass/fail summary.
- Results and analysis from regression testing.
- Responses to test failures, including any corrective actions taken and verification of those changes.
For Enhanced level
- All Basic level documentation.
- Unit level test protocol and report with expected vs. actual results and pass/fail.
- Integration level test protocol and report with expected vs. actual results and pass/fail.
IEC 62304 Sources: Relevant sections of IEC 62304 include:
- 5.5 - Software unit implementation and verification
- 5.6 - Software integration and integration testing
- 5.7 - Software system testing
Key Elements: Your software testing documentation should include test plans, test cases, test results, requirement to test case traceability matrix, regression testing data, bug tracking documentation, etc.
Critical: The FDA is very interested in seeing that all requirements have been covered by verification and as a result you will need to have documentation that shows traceability from a requirement to a test case and the final result of that specific test case, where testing is the verification method.
Document 9: Software Version/Revision Level History
Purpose: Provide a complete history of tested and released software versions.
Content Requirements: Provide a complete history of tested software versions going back to when design controls were implemented. The history should list the software test date, a unique identifier (i.e., software version number), and a brief description of changes made. The final line of the history should be for the final software version to be incorporated in the released device, and any descripive differences between this and prior tested versions should be explained for any effect on safety or effectiveness. Also, describe which prior software versions have been cleared or otherwise approved (including submission numbers). (Preferably in a spreadsheet format, the final line should reflect the final software version to be incorporated in the released device).
IEC 62304 Sources: This documentation draws on IEC 62304 ( sections 5.8 and 8).
Key Elements:
- Software version numbering scheme
- Software release notes
- Verification status for each software version
- Description of changes made to this software version
Practical Tip: this document should be maintained throughout the life of the device, it’s not something to create near the end when you realize you need it.
Document 10: Unresolved Software Anomalies
Purpose: Provide a list of all known software bugs that have not been corrected, and assess the impact that they may have on safety and effectiveness of the device.
Content Requirements:
- Description of each as-yet-unresolved software bug
- How the bugs were found
- Root cause of the bugs, where known
- Assessment of the effect of each bug on safety and device effectiveness
- Rationale (with supporting risk analysis) for why the bugs do not need to be corrected immediately
- Instructions for dealing with the bugs (including any workarounds and cautions that have been communicated to users)
IEC 62304 Sources: 9 (Software problem resolution process)
Key Elements: List of bugs by severity, impact/risk assessment (as per the risk management file), justification for deferral, user instructions.
Important: If there are no unresolved software bugs, be sure to state this explicitly in your submission. (The official guidance does not specify what to do in this case, and reviewers need to see "no unresolved software bugs" rather than a missing document.)
Practical Tip: For clarity and consistency, consider classifying software bugs using a recognized standard such as ANSI/AAMI SW91.
Beyond Software: Cybersecurity Documentation Requirements
Cyber devices are subject to requirements related to the cybersecurity plan, SBOM, and other processes under Section 524B of the FD&C Act.
However, FDA’s February 2026 premarket cybersecurity guidance recommends a cybersecurity documentation package in addition to software development lifecycle documentation for devices with cybersecurity considerations. Its Appendix 4 Table 1 explains six documentation types, organized into a total of fourteen elements. These include a cybersecurity risk management report (e.g. describing the threat model, risk assessment, SBOM, vulnerability assessment, any unresolved anomalies, and traceability matrix), measures of effectiveness and performance, architecture view(s), testing documentation, labeling information, and a cybersecurity management plan.
These documents, separate from but related to software lifecycle documentation, describe the steps you take (both before marketing and thereafter) to manage cybersecurity risks throughout the device’s lifecycle. They also document your device’s cybersecurity architecture and how you identify and respond to post-market cybersecurity vulnerabilities. Our book covers each of these artifacts document by document, starting with the cybersecurity story FDA expects your submission to tell.
For comprehensive background on cybersecurity requirements:
- For a complete list of software and cybersecurity documentation FDA recommends: Documents FDA Requires for Software and Cybersecurity
- For the approach to performing a cybersecurity risk assessment: Complete Guide to FDA Cybersecurity Risk Assessment
- For regulatory expectations for medical device cybersecurity: FDA Cybersecurity Requirements for Medical Devices
- For the guidance update: FDA's 2026 Cybersecurity Guidance Update
eSTAR documents are not a replacement for a thorough understanding of FDA regulations and guidance related to medical device software and cybersecurity. The documents you submit to the FDA are essential parts of the regulatory puzzle, but they are not the whole picture. Be sure to read both categories of guidance so you fully understand the expectations of the FDA.
If your device contains software, make sure to familiarize yourself with all of the software-related documents the FDA expects to receive. If your device also has cybersecurity risks, you’ll need to address those expectations as well. If you’re unsure where to start, take at your list of expected documents, and start matching each of the eight life cycle stages of IEC 62304 to that list.
How does IEC 62304 Clause 5 map to eSTAR documents?
As outlined in IEC 62304, there are eight parts (Clause 5.1 - 5.8) to the software development process. Unlike the eight steps in IEC 62304, the eSTAR format does not provide a step- by-step approach to medical device software development. Rather, it focuses on the documentation needed to support the development process and demonstrate compliance with FDA regulations.
The Development Process Flow
The stages can be revisited as development progresses:
- 5.1 Software development planning: Covers the ins and outs of your development approach, needed resources, and plans.
- 5.2 Software requirements analysis: Details exactly what your software shall do.
- 5.3 Software architectural design: determines how software will be structured
- 5.4 Software detailed design: specifies implementation details for software units
- 5.5 Software unit implementation and verification: codes and verifies individual units
- 5.6 Software integration and integration testing: units are combined and interface is tested
- 5.7 Software system testing: verifies complete software against requirements
- 5.8 Software release: prepares software for delivery
Stages have specific inputs, activities, and outputs; the outputs can be used in your eSTAR documentation.
Direct Process-to-Document Mapping
| IEC 62304 Process Stage | eSTAR Documents Produced |
|---|---|
| 5.1 Development Planning | Software Development, Configuration Management, and Maintenance Practices (summary of lifecycle processes) |
| 5.2 Requirements Analysis | Software Requirements Specification |
| 5.3 Architectural Design | Software Description; System and Software Architecture Design Chart; Risk Management File (architectural analysis feeds risk assessment) |
| 5.4 Detailed Design | Software Design Specification (Enhanced only) |
| 5.5 Unit Implementation | Software Development, Configuration Management, and Maintenance Practices; Software Testing Documentation (unit tests) |
| 5.6 Integration Testing | Software Testing Documentation (integration tests) |
| 5.7 System Testing | Software Testing Documentation (system tests) |
| 5.8 Software Release | Software Version History; Unresolved Software Anomalies |
The Critical Integration Point
The IEC62304 Section 7.1 "Analysis of software contributing to hazardous situations" relates to several e-star documents and connects with the architectural design work in Section 5.3. It informs the software description by identifying "safety critical functions/category of functions that need to be described", fills the risk management file in by providing software-related hazards and hazardous situations and supports the "Documentation Level Evaluation" by providing evidence relevant to the software’s contribution to patient risk.
This is an integration between a lifecycle standard (IEC62304) and practical documents (e-star). It is the link that provides the consistency needed in your submission to demonstrate you have followed a systematic approach.
No duplicate documentation needed
When you follow a systematic approach (IEC62304), many of the e-star documents can "fall out" naturally. You can reuse development records for the FDA when they contain the recommended information. You correctly develop and present the relevant design and development file records (the DHF under the former regulation). It is therefore extremely important to develop a clear documentation strategy from the beginning of your project, not "retrofit" documents for the FDA at the end of the project.
Practical Implementation Strategies
Strategy 1: Design Your Documentation Structure Early
Don’t wait until you’re ready to submit to format your documents to meet FDA expectations. Instead, during project planning, create templates for the documentation you need to meet both IEC 62304 and eSTAR requirements.
Implementation:
- Use a requirements template that maps directly to functional, performance, safety, and security requirements expected by the FDA.
- Use a risk management file structure that satisfies both ISO 14971 and FDA submission requirements.
- Use a consistent ID structure (REQ-XXX, DESIGN-XXX, TEST-XXX, RISK-XXX) and a requirements traceability matrix template (linking requirements to design, to test cases, to risks).
Benefit: This can reduce reformatting work at submission time, because the documentation structure already addresses FDA expectations.
Example: Instead of creating requirements in developer-friendly format then reformatting for FDA, write requirements in FDA-compatible format from day one. It can satisfy both needs simultaneously.
Strategy 2: Maintain Living Documents
Incorporate documentation into the development lifecycle, rather than creating it en masse at the end.
Implementation:
- Establish a documentation review process. Require that requirements be reviewed before design, design before code.
- Put all documents under source control, not just code.
- Make regular documentation reviews (e.g., weekly or biweekly) part of your team’s rituals. The goal is to catch gaps early and incorporate documentation as part of the definition of done for development activities.
Benefit: Better prepared for submission. Less scrambling to reconstruct decisions made months ago. Can support faster cycles for FDA review if/when they have questions.
Reality Check: While this takes discipline, retroactive documentation takes longer and is more susceptible to errors. It also sets your team up for failure if the documentation doesn’t line up with the actual development timing.
Strategy 3: Use Your Quality Management System
Many eSTAR-recommended pieces of documentation exist as part of other QMS processes. Reference QMS process documents (e.g., configuration and change management) rather than duplicating them, where this provides the recommended submission content.
Implementation:
- Configuration Management: reference your QMS config control procedure and give section numbers.
- Change Management: reference your QMS design change control SOP.
- Development processes: reference QMS procedures (e.g., design controls, verification, validation).
- Create summary documents that reference the detailed procedures instead of reproducing them, where summaries are appropriate for the documentation level.
Benefit: Reduces the amount of documentation your team has to develop and maintain. Avoids redundancy of processes.
Example: For a Basic-level summary, instead of reproducing a 20-page configuration management plan, develop a 2-page summary: Configuration Management follows [Company] SOP-123 Design Control, section 4.5. Version control follows [Company] SOP-456 Document Control, section 3.2, etc...
Strategy 4: Create Bidirectional Traceability
FDA reviewers are looking for traceability throughout your documentation packet so it’s best if you implement it in a systematic way. This includes
Implementation:
- Forward traceability from requirements to design, code and tests
- Backward traceability from requirements to system requirements and risks
- Tests traceability to requirements that they verify
- Risk controls traceability to requirements that implement them and tests that verify them
Traceability matrices (which map these relationships) can often be generated automatically by tools, consider using these if possible to save time.
Benefit: Complete traceability helps demonstrate completeness, helps assess impact of changes and can be referred to if an FDA reviewer asks how a requirement or test covers a certain risk.
Tool Tip: Traceability matrices with thousands of lines become difficult to manage in a spreadsheet, a requirements management tool may be better suited for larger projects.
Common Pitfalls to Avoid
- Starting documentation at development end. Start documentation early: You’ll need to do documentation throughout development, not after. The FDA will also want to see documentation of your design process. By leaving this to the end, your design documentation may not match the order you actually went through to develop the software.
- Creating separate "FDA" and "IEC 62304" documents. Combine your FDA and IEC 62304 documentation: While it might be tempting to keep separate FDA and IEC 62304 document sets, it’s a lot of work and prone to inconsistencies. One documentation set, carefully planned to meet the needs of both, is easier and more effective.
- Inadequate traceability between documents. Traceability: The FDA will be looking closely at traceability, including from requirements to risk mitigations to testing, so having a plan and traceability matrices in place from day one will help.
- Forgetting the Documentation Level rationale. Decide on documentation level and justify it: The FDA will be looking for documentation level justification and may want you to continue at a higher documentation level than originally decided upon. Be prepared to defend your documentation level decisions with supporting material, such as risk assessment data, and update the level if the assessment changes.
- Missing safety-security integration points. Address security and risk assessment integration in your software architecture: The FDA will look for security built into your software architecture and a clear link back to risk assessment and hazard analysis. Make sure to include analysis of software contributing to hazardous situations alongside your architecture design and clear documentation in the risk files.
Conclusion
When developing medical device software it's important to understand the relationship between IEC 62304 (the standard that defines the life cycle requirements for medical device software) and FDA eSTAR requirements. IEC 62304 supports development of records used in eSTAR submissions, but following it alone does not establish that all FDA submission recommendations have been addressed.
Key takeaways
- Two Documentation Levels: A key difference between eSTAR and IEC 62304 is documentation level: eSTAR uses 2 FDA documentation levels, BASIC and ENHANCED. FDA recommends 10 documentation items at ENHANCED and 9 at BASIC, with SDS submission documentation added at Enhanced and more detailed configuration management and testing information. The level is based on the probable-risk assessment described above. IEC 62304 does not set these FDA documentation levels or decide whether an SDS should be submitted to FDA.
- Direct Process Mapping: One good news is that IEC 62304 can be used to support FDA eSTAR documentation. As you systematically develop software according to IEC 62304 you can produce much of the documentation used to address eSTAR recommendations.
- Single Development Process: There's no need for a separate development process for each. One process can support both, with documentation checked against FDA’s submission recommendations.
- Critical Integration: "Analysis of software contributing to hazardous situations" under IEC 62304 Section 7.1 integrates information from other deliverables, particularly Risk Management File, Software Architecture, and SDS. It supports Software Description and can inform the Documentation Level Evaluation, but the FDA level remains a separate probable-risk decision.
Practical next steps
- Determine Your Documentation Level: It's good practice, however, to explicitly state the documentation level you'll be using and also the rationale for that determination, tied back to risk.
- Map Your Existing Documentation: Since one process can be used to meet both eSTAR and IEC 62304 requirements, it's useful to map one to the other up front to identify any gaps.
- Establish Templates and Traceability: Document once, use for both where the content is adequate, and therefore establish templates and a traceability approach to simplify future software development projects.
- Implement Living Documentation: Think of documentation as something that's done proactively, rather than reactively. By proactively developing documentation (and living documentation, that gets updated as software changes) it can simplify preparation for FDA review as documentation is already available to support review.
Medical device software documentation doesn't have to be painful. When IEC 62304 and FDA expectations align through proper planning, documentation can become a natural byproduct of good development practice rather than a burdensome afterthought. The key is understanding the mapping and implementing it systematically from project inception.
Need help with your IEC 62304 documentation or eSTAR software section? Email us at info@cybermed.ai.
Sources
- FDA. Content of Premarket Submissions for Device Software Functions. Final guidance, June 14, 2023. https://www.fda.gov/regulatory-information/search-fda-guidance-documents/content-premarket-submissions-device-software-functions
- FDA. Cybersecurity in Medical Devices: Quality Management System Considerations and Content of Premarket Submissions. Final guidance, February 3, 2026. https://www.fda.gov/regulatory-information/search-fda-guidance-documents/cybersecurity-medical-devices-quality-system-considerations-and-content-premarket-submissions
- IEC 62304:2006 + A1:2015. Medical device software, Software life cycle processes. https://www.iso.org/standard/38421.html
- ISO 14971:2019. Medical devices, Application of risk management to medical devices. https://www.iso.org/standard/72704.html
- ANSI/AAMI SW91:2018. Classification of defects in health software.
Frequently asked questions
›How many software documents does FDA expect in an eSTAR submission?
FDA's software guidance lists ten documentation elements. Nine apply at the Basic documentation level and all ten at Enhanced. Enhanced adds the Software Design Specification plus complete configuration management and maintenance plans and unit and integration test protocols with reports, rather than summaries.
›How do I know if my device needs Basic or Enhanced documentation?
It hinges on one question from FDA's 2023 software guidance: could a failure or flaw of the device software function present a probable risk of death or serious injury? You evaluate the raw, unmitigated risk before risk controls. Yes means Enhanced, no means Basic. FDA also recommends Enhanced for all Class III devices and drug/device combination products.
›Do I need separate documentation for IEC 62304 and FDA?
No. Following IEC 62304 systematically produces the eSTAR software documents as natural outputs of development. The trick is intentional documentation structure from project start, so a single documentation set satisfies both.
›Which IEC 62304 clauses map to which eSTAR documents?
Clause 5.2 (requirements analysis) produces the SRS, 5.3 (architectural design) produces the Software Description and architecture chart, 5.4 (detailed design) produces the SDS for Enhanced level, 5.5 through 5.7 produce the testing documentation, and 5.8 (release) produces the version history and unresolved anomalies list.
›Does the eSTAR software documentation cover FDA's cybersecurity requirements too?
No. The software documents cover the software lifecycle. FDA's February 2026 cybersecurity guidance asks for a separate cybersecurity package. Its Appendix 4 Table 1 lists six documentation types broken into fourteen elements, covering the threat model, risk assessment, SBOM, architecture views, testing, labeling, and management plans. The two packages are separate but complementary.